blog

Identity Takeaways from Fal.Con 2026

September 14, 2026

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

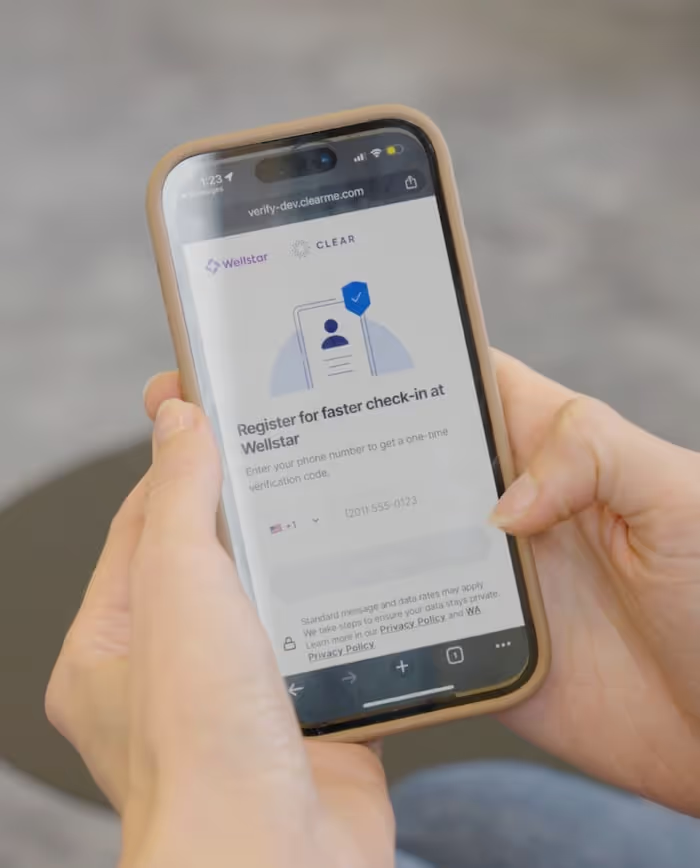
In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

Maximize security, minimize friction with CLEAR

Reach out to uncover what problems you can solve when you solve for identity.

By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
blog

Identity Takeaways from Fal.Con 2026

September 14, 2026

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

Maximize security, minimize friction with CLEAR

Reach out to uncover what problems you can solve when you solve for identity.

By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
blog

Identity Takeaways from Fal.Con 2026

September 14, 2026

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

Maximize security, minimize friction with CLEAR

Reach out to uncover what problems you can solve when you solve for identity.

By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
blog

Identity Takeaways from Fal.Con 2026

September 14, 2026

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

More product updates

VIEW ALL RELEASE NOTES
No items found.
blog

Identity Takeaways from Fal.Con 2026

September 14, 2026

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

blog

Identity Takeaways from Fal.Con 2026

September 14, 2026

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

What Fal.Con 2026 taught us about identity and its role in securing behavior during the AI Revolution


Last week, more than 10,000 cybersecurity leaders and technology partners came together for CrowdStrike’s annual Fal.Con conference to explore how security must evolve for the AI era. This year’s theme, “Securing the AI Revolution,” captured the urgency of that challenge as increasingly sophisticated AI-driven attacks make impersonation and social engineering easier than ever.

Across keynotes, sessions, and conversations, one message came through clearly: the agentic era is already here. Organizations are managing a growing mix of human and machine identities, each of which must be appropriately verified and governed. And as AI agents take on more authority, establishing trust in the real people behind consequential activity becomes even more important.

We were excited to explore these questions alongside the broader Fal.Con community. Through a featured speaking session, events with GuidePoint Security, and the announcement of a new integration between CLEAR1 and the CrowdStrike Falcon® platform, we explored how high-assurance identity signals can give defenders greater context to understand and respond to emerging risks.

Connecting Identity with Threat Detection in the CrowdStrike Falcon Platform

Announced at Fal.Con, the CLEAR and CrowdStrike integration brings CLEAR1’s person-based verification into Falcon risk detection platforms—giving security teams an additional layer of identity context when suspicious activity is detected.

Attackers increasingly use stolen credentials, social engineering, and legitimate access pathways to blend into normal activity. But a valid credential or recognized device is not the same as a verified person. By bringing person-based verification together with intelligent threat detection, security teams can make faster, more informed decisions without introducing unnecessary friction into every interaction.

In practice, when Falcon detects potential risk, a CLEAR1’s secure identity verification can be triggered to verify the person in real time, which includes capturing biometrics and government-issued identification and verifying it against authoritative sources. That verification result can then be considered alongside other security signals to inform an investigation or response. By correlating identity verification data with signals across the Falcon platform, security teams can distinguish legitimate users from potential bad actors and uncover suspicious patterns that may be difficult to recognize when signals are viewed in isolation.

What Fal.Con Reinforced About Workforce Identity


During CLEAR’s speaking session, CLEAR CSO, Jon Schlegel, GuidePoint Field CISO, Emily O'Carroll, and Okta VP of AI Agents & Identity Security, Nick Davis, examined what these broader shifts mean for workforce identity and how person-based verification can help organizations better understand and respond to risk. Three takeaways stood out:

  1. Workforce identity assurance must be multi-layered and embedded in moments that matter
    Identity risk does not begin and end at login. It can emerge during onboarding, privilege changes, account recovery, help-desk interactions, third-party access, or the use of sensitive systems. 

    A more dynamic approach connects these moments and applies more assurance across touchpoints where the stakes are highest. This allows organizations to protect critical actions without adding the same level of friction to every workflow—and helps security teams work from a more complete security context.

  1. Verifying and securing behavior starts with knowing who’s behind it
    AI-driven threats are making it harder to distinguish legitimate users from sophisticated impersonation. Security teams may be able to identify anomalous behavior, but detecting an anomaly does not always answer a critical question: Is the person taking the action really who they claim to be?

    Person-based identity verification helps close that gap. When higher assurance is needed, organizations can establish greater confidence in the individual behind an account or device and use that information to determine whether an action should proceed, be investigated, or be blocked.

    This turns identity from a static access check into a dynamic security signal—one that can help teams take more precise action when responding to a threat signal.

  1. Correlated cross-platform signals are critical for outpacing AI-driven fraud
    No single signal provides the full picture of identity risk. The CLEAR1 and CrowdStrike integration demonstrates the value of connecting identity assurance with the security systems already detecting and responding to risk.

    Embedding verification data into risk detection workflows proves that the best solution is not another isolated check. It is a connected view of identity and behavior across the systems that shape access—including HR, identity and access management, IT service management, and help-desk workflows. 

    When signals remain fragmented, activity can look legitimate within individual systems. When they are connected, teams can identify patterns that are otherwise easy to miss and apply the right level of response.

Looking Ahead


Fal.Con reinforced that the agentic era is no longer theoretical. As AI reshapes enterprise workflows and the threat landscape, organizations need greater confidence not only in the activity they observe, but in the people behind consequential actions. That requires moving beyond credentials and devices alone toward a multi-layered approach to identity assurance.

It also requires connected ecosystems. Following the introduction of the CLEAR Partner Program, Fal.Con was an opportunity to demonstrate how trusted identity can work alongside the cybersecurity tools, teams, and workflows organizations already rely on. 

In the AI era, detecting suspicious behavior isn’t enough. Verifying the person behind the signal is the key to turning detection into action.

PARTNER SPOTLIGHT
INDUSTRY
Workforce
COMPANY SIZE
INDUSTRY
Workforce
COMPANY SIZE

Maximize security, minimize friction with CLEAR

Reach out to uncover what problems you can solve when you solve for identity.

By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
blog
Person looking at CLEAR Multi-Layered Identity Screen
By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
Gartner®, Deepfake Identity Threats: Mitigate Risk in Identity Verification and Face Biometrics, Akif Khan, Nayara Sangiorgio, James Hoover, 11 May 2026

Gartner® is a trademark of Gartner, Inc. and/or its affiliates.
blog
By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
Thank you! You are being redirected

Thank you! View the webinar below.

Oops! Something went wrong while submitting the form.
blog

Identity Takeaways from Fal.Con 2026

September 14, 2026

More webinars

VIEW ALL WEBINARS
No items found.