blog

How Identity Fraud Enters Through Your Workforce

October 28, 2026

Key Takeaways

  • Enterprise fraud is different from consumer identity theft: an attacker can use a legitimate person’s identity to enter the organization, receive access, or recover an account.
  • Three critical workflows are onboarding, help desk recovery, and self-service account recovery. Each workflow can grant or restore workforce access.
  • Identity security protects accounts, credentials, and access. Identity verification helps establish who’s requesting access or account recovery.
  • A verified workforce identity combines document checks, biometric matching, liveness detection, and other signals during onboarding, recovery, and high-risk actions.
  • CLEAR1 verifies the person at onboarding and re-verifies identity during help desk recovery or self-service resets, helping organizations confirm that the person using the credential is the person it was issued to.

What Identity Fraud Looks Like Inside an Enterprise

‍

Workforce identity fraud occurs when someone uses stolen or fabricated identity information, compromised credentials, or false employment details to gain access to an organization or its systems.

‍

Consumer identity theft often involves opening accounts or obtaining services in another person’s name. In an enterprise, attackers can exploit hiring, support, or recovery workflows to obtain workforce access—even when the account looks normal and the credential is valid.

‍

Identity security protects accounts, credentials, and access through controls such as workforce identity and access management. Identity verification confirms who a person is before organizations grant access or approve a high-risk action. Authentication checks whether someone can present an enrolled credential, but doesn’t establish that the right person enrolled the account or is requesting recovery.

‍

These identity checks matter before suspicious activity appears. By the time detection tools raise an alert, an attacker may already have passed through hiring or persuaded the help desk to restore access.

‍

Why the Workforce is the Entry Point

‍

Attackers don’t always need to steal a password or bypass MFA. Weak identity checks during hiring or account recovery can lead an organization to issue valid credentials to an impostor.

‍

Protecting accounts and devices doesn’t replace verifying the employees, contractors, and vendors requesting access. Even with phishing-resistant authentication, organizations still need to answer three critical identity questions:
‍

  • Is the person applying for a role the person they claim to be?
  • Is the person requesting an MFA factor replacement authorized to make that request?
  • Is the person requesting account recovery the person who should receive a new credential?

‍

Three Common Moments Where Fraud Enters the Workplace


Three workflows deserve particular attention: onboarding, when organizations grant access; help desk recovery, when agents decide whether to restore access; and self-service recovery, when systems restore access without an agent. Each workflow starts with a claim about who the person is. Identity verification helps confirm that the person requesting access is who they say they are.

‍

1. Onboarding


Document reviews, video interviews, and work eligibility checks don’t necessarily establish that the person interviewed is the person who ultimately receives access. This leaves organizations vulnerable to fraudulent applicants, interview substitution, synthetic or deepfaked candidates, and impersonated contractors.

‍

Remote hiring fraud is a documented risk, not a hypothetical one. In a July 31, 2026 joint alert, the U.S. State Department, FBI, and international partners warned that North Korean IT workers use forged identity documents and third-party proxies to obtain remote work. Proxies may even participate in interviews while someone else performs the job. The alert urges online employment and contracting platforms to strengthen identity verification procedures. 

‍

A verified onboarding flow, as part of a broader Know Your Employee approach, connects the person to the identity document, confirms that a live person is present, and checks supporting signals before provisioning access. This matters in cases of synthetic identity fraud, where attackers combine real and fabricated information to create an identity that appears legitimate.

‍

2. Help Desk Recovery


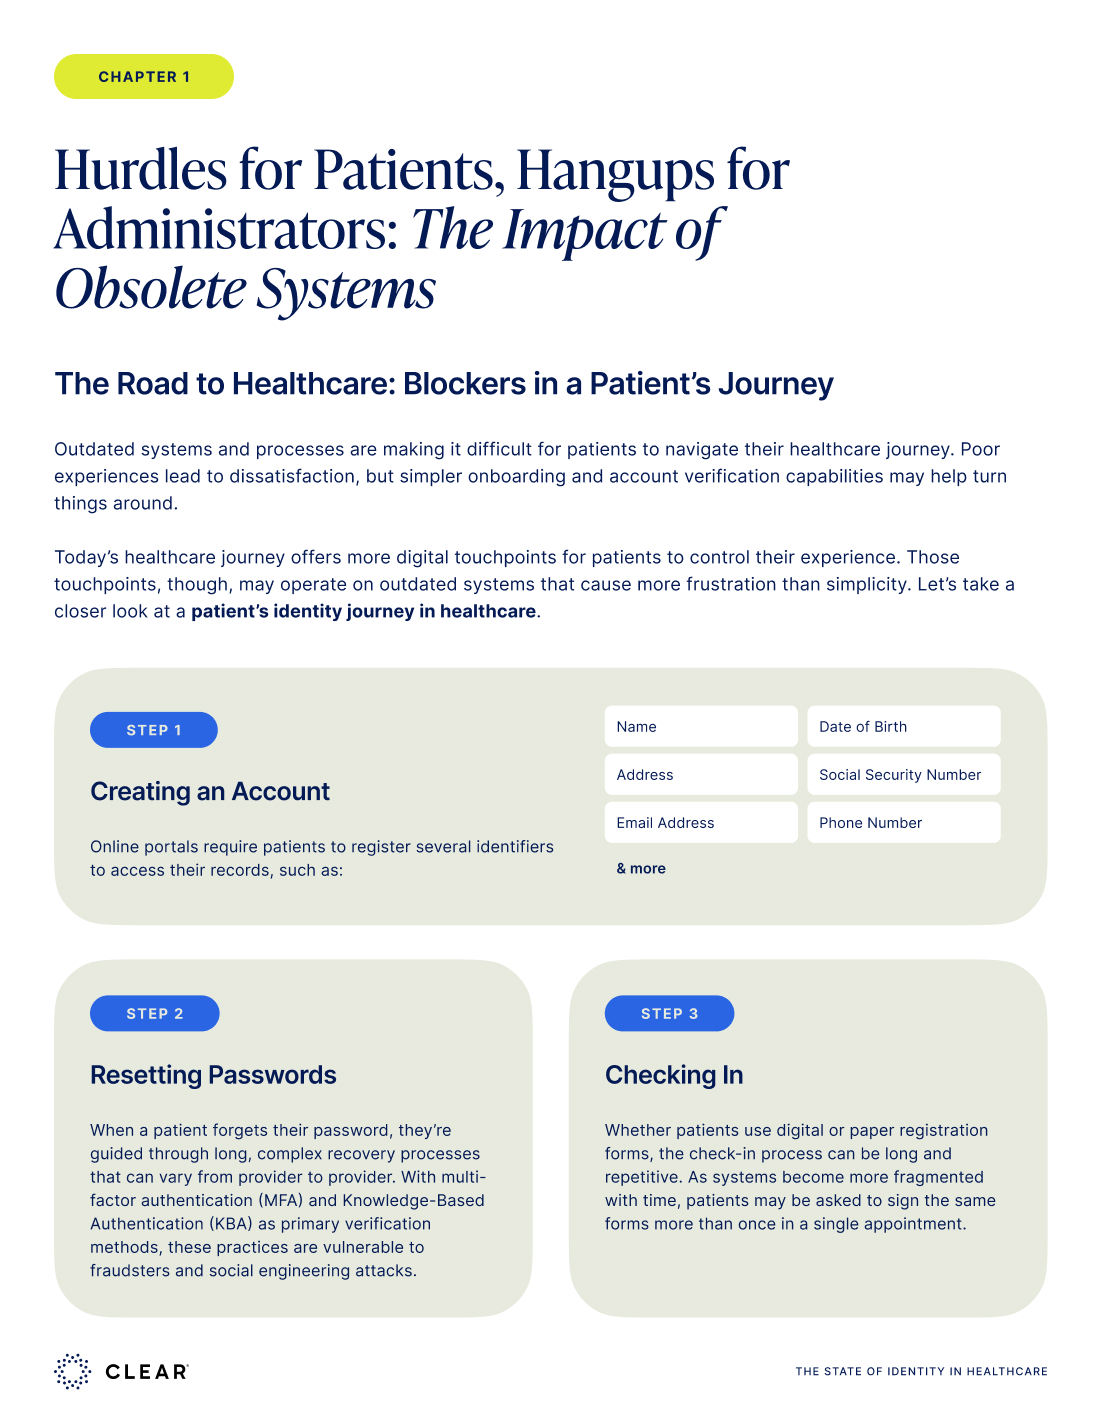
Help desks may ask for an employee ID, manager’s name, start date, or the last four digits of a government identifier. Those answers can show familiarity with an employee’s information without establishing the caller’s identity.

‍

Social engineering exploits the pressure to restore access quickly. The workflow asks help desk agents to make an identity decision with weak evidence.

‍

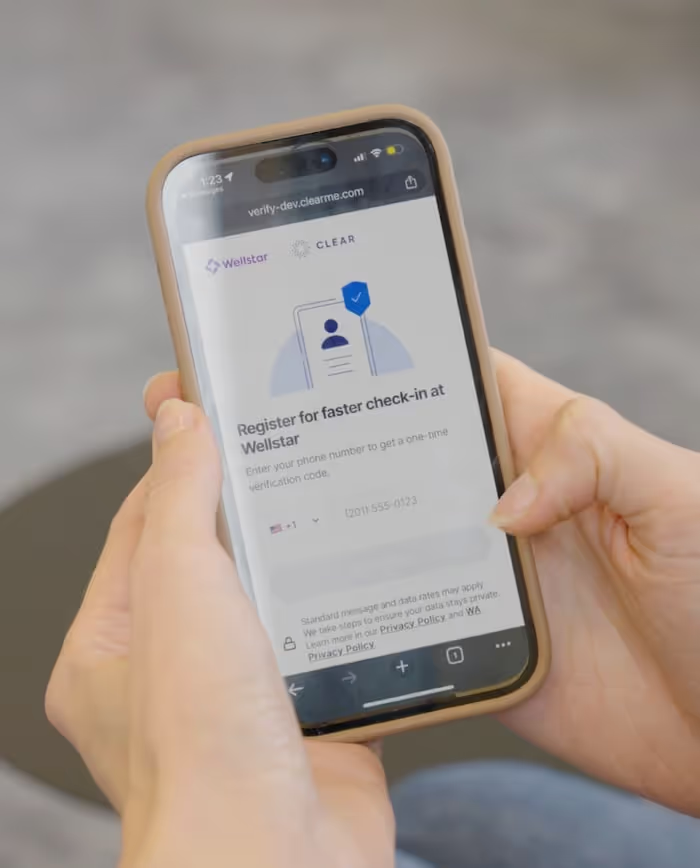
Rather than rely on those answers alone, the help desk agent can initiate document and selfie verification before restoring access. The caller presents a government-issued document and takes a selfie. The system checks document authenticity, liveness, and whether the selfie matches the document photo. The agent can then apply the organization’s recovery policy using verified identity information rather than answers to personal questions.

‍

3. Self-Service Account Recovery


Self-service recovery exists because users forget passwords or lose access to phones, security keys, or authenticator apps. But if the process relies on a compromised mailbox, an attacker-controlled phone number, a stolen backup code, or a security question the attacker can answer, the attacker can reset credentials and take over the account.

‍

When normal authentication fails, organizations should verify the person requesting account recovery before restoring access. Depending on the risk, verification can include document checks, biometric matching, liveness detection, source validation, and device security signals. Stronger identity checks are particularly important before replacing an MFA factor or changing a recovery channel, especially for privileged accounts.

‍

Why MFA Can’t Verify the Person Behind the Credential


MFA, passwordless sign-in, and phishing-resistant methods strengthen account security, but stronger authentication won’t fix access granted to the wrong person. An impostor may still pass through onboarding. An attacker may still persuade the help desk to reset someone else’s sign-in method. Organizations need identity verification to help confirm that the person receiving access or requesting a change is the person they intended to authorize.

‍

What Verified Workforce Identity Means in Practice


Verified workforce identity means establishing who a person is when the organization issues access, then re-verifying that identity before high-risk actions. Organizations should choose identity checks based on the action’s risk and retain a record of the verification result.

‍

A practical identity verification flow can include:
‍

  • Government-issued document verification to check authenticity and signs of tampering.
  • A selfie matched to the document portrait to connect the person presenting the document to the claimed identity.
  • Liveness, presentation-attack detection, and injection attack detection to help confirm that a real person is present rather than a photo, replay, mask, or injected image.
  • Source and device signals that add evidence when the workflow requires more than a document and selfie.

‍

These capabilities provide a starting point for comparing employee identity verification solutions for onboarding and account recovery.

‍

Assurance frameworks can help define requirements for these workflows: IAL2 addresses identity proofing, while AAL2 addresses authentication. Organizations still need clear policies for when to verify identity, how to handle data, and how to act on verification results.

‍

Ultimately, no single check establishes identity on its own. A multi-layered approach to identity proofing evaluates the signals together to help confirm that a live person matches the claimed identity and that the supporting information is consistent.

‍

Workforce Identity Verification Across the Employee Lifecycle


Not every action requires identity re-verification. Organizations should apply stronger checks when unauthorized access could expose sensitive data, move money, or change critical systems.

‍

  • Hire: Verify the person before the organization creates a workforce identity, especially for remote, contractor, vendor, and sensitive-role onboarding.
  • First-day provisioning: Use the onboarding verification result to confirm who receives the device, account, or authenticator.
  • Privileged or financial actions: Step up identity assurance before an administrator changes production access, a finance user changes payment details, or an executive account performs a sensitive action.
  • Help desk recovery: Re-verify the caller before resetting a password, replacing an MFA factor, or changing a recovery channel.
  • Contractor and vendor access: Apply a clear, risk-based policy instead of assuming that third-party status justifies weaker proofing.

‍

Organizations can use employee verification to match each stage of the workforce lifecycle with the identity checks it requires. The goal is to verify identity before granting access, restoring access, or approving sensitive changes—not before every action.

‍

Questions to Ask About Your Own Environment

‍

  • What does our help desk verify before the team resets a password or replaces an MFA factor?
  • How did we verify the identities of our last 50 hires, and what evidence do we retain?
  • What happens when an employee loses every authentication factor at once?
  • Which actions trigger re-verification before a privileged account, payment workflow, or recovery channel changes?

‍

How CLEAR1 Verifies Workforce Identity


CLEAR1 strengthens workforce security by verifying the person beyond the device. Its multi-layered approach combines biometric, document, and device signals with verified data sources to help confirm that employees and contractors are who they claim to be—during onboarding, account recovery, and other critical workforce moments.

‍

After a one-time setup, people can re-verify with a selfie when they need help restoring access or completing a sensitive action. Organizations can confirm identity again without requiring people to repeat the full document-verification process.

‍

Through integrations with leading IAM platforms and enterprise systems, CLEAR1 brings these checks into the tools teams already use. This approach extends workforce identity assurance beyond onboarding to help desk support, account recovery, and privileged access—without replacing existing infrastructure.

‍

Request a CLEAR1 demo

Frequently Asked Questions

What is workforce identity fraud?

Workforce identity fraud occurs when someone uses stolen or fabricated identity information, compromised credentials, or false employment details to gain access to an organization or its systems. Attackers can exploit hiring, contractor onboarding, help desk recovery, or self-service resets to obtain workforce access.

‍

What are the most common types of identity fraud in the workplace?

Common forms include fraudulent applicants, interview substitution, synthetic identities, contractor impersonation, help desk social engineering, compromised recovery channels, and account takeover. These attacks can exploit gaps in how organizations establish identity, protect accounts, and verify requests to restore access.

‍

What is an identity-based attack?

An identity-based attack uses a person’s account, credential, identity data, or recovery path to gain access. Strong defenses combine authentication with identity verification, device and session signals, access controls, and re-verification for high-risk actions.

‍

How do attackers use social engineering against IT help desks?

Attackers impersonate employees, create urgency, and use public profiles, breached data, or compromised accounts to answer routine questions. Knowledge-based checks can lead to a password reset or new MFA factor. Document-and-selfie verification gives the agent stronger evidence.

‍

Can MFA prevent account takeover?

MFA can prevent many account takeover attempts, but it doesn’t verify who enrolled the account. A weak recovery channel can still replace a lost factor without confirming the account holder. Pair MFA with identity verification at onboarding and before high-risk resets, factor changes, or privileged access decisions.

‍

How do companies verify remote employees during onboarding?

Companies can verify remote employees by checking a government-issued document, matching a live selfie to the document portrait, confirming liveness, and applying device or source signals when needed.

What Identity Fraud Looks Like Inside an Enterprise

‍

Workforce identity fraud occurs when someone uses stolen or fabricated identity information, compromised credentials, or false employment details to gain access to an organization or its systems.

‍

Consumer identity theft often involves opening accounts or obtaining services in another person’s name. In an enterprise, attackers can exploit hiring, support, or recovery workflows to obtain workforce access—even when the account looks normal and the credential is valid.

‍

Identity security protects accounts, credentials, and access through controls such as workforce identity and access management. Identity verification confirms who a person is before organizations grant access or approve a high-risk action. Authentication checks whether someone can present an enrolled credential, but doesn’t establish that the right person enrolled the account or is requesting recovery.

‍

These identity checks matter before suspicious activity appears. By the time detection tools raise an alert, an attacker may already have passed through hiring or persuaded the help desk to restore access.

‍

Why the Workforce is the Entry Point

‍

Attackers don’t always need to steal a password or bypass MFA. Weak identity checks during hiring or account recovery can lead an organization to issue valid credentials to an impostor.

‍

Protecting accounts and devices doesn’t replace verifying the employees, contractors, and vendors requesting access. Even with phishing-resistant authentication, organizations still need to answer three critical identity questions:
‍

  • Is the person applying for a role the person they claim to be?
  • Is the person requesting an MFA factor replacement authorized to make that request?
  • Is the person requesting account recovery the person who should receive a new credential?

‍

Three Common Moments Where Fraud Enters the Workplace


Three workflows deserve particular attention: onboarding, when organizations grant access; help desk recovery, when agents decide whether to restore access; and self-service recovery, when systems restore access without an agent. Each workflow starts with a claim about who the person is. Identity verification helps confirm that the person requesting access is who they say they are.

‍

1. Onboarding


Document reviews, video interviews, and work eligibility checks don’t necessarily establish that the person interviewed is the person who ultimately receives access. This leaves organizations vulnerable to fraudulent applicants, interview substitution, synthetic or deepfaked candidates, and impersonated contractors.

‍

Remote hiring fraud is a documented risk, not a hypothetical one. In a July 31, 2026 joint alert, the U.S. State Department, FBI, and international partners warned that North Korean IT workers use forged identity documents and third-party proxies to obtain remote work. Proxies may even participate in interviews while someone else performs the job. The alert urges online employment and contracting platforms to strengthen identity verification procedures. 

‍

A verified onboarding flow, as part of a broader Know Your Employee approach, connects the person to the identity document, confirms that a live person is present, and checks supporting signals before provisioning access. This matters in cases of synthetic identity fraud, where attackers combine real and fabricated information to create an identity that appears legitimate.

‍

2. Help Desk Recovery


Help desks may ask for an employee ID, manager’s name, start date, or the last four digits of a government identifier. Those answers can show familiarity with an employee’s information without establishing the caller’s identity.

‍

Social engineering exploits the pressure to restore access quickly. The workflow asks help desk agents to make an identity decision with weak evidence.

‍

Rather than rely on those answers alone, the help desk agent can initiate document and selfie verification before restoring access. The caller presents a government-issued document and takes a selfie. The system checks document authenticity, liveness, and whether the selfie matches the document photo. The agent can then apply the organization’s recovery policy using verified identity information rather than answers to personal questions.

‍

3. Self-Service Account Recovery


Self-service recovery exists because users forget passwords or lose access to phones, security keys, or authenticator apps. But if the process relies on a compromised mailbox, an attacker-controlled phone number, a stolen backup code, or a security question the attacker can answer, the attacker can reset credentials and take over the account.

‍

When normal authentication fails, organizations should verify the person requesting account recovery before restoring access. Depending on the risk, verification can include document checks, biometric matching, liveness detection, source validation, and device security signals. Stronger identity checks are particularly important before replacing an MFA factor or changing a recovery channel, especially for privileged accounts.

‍

Why MFA Can’t Verify the Person Behind the Credential


MFA, passwordless sign-in, and phishing-resistant methods strengthen account security, but stronger authentication won’t fix access granted to the wrong person. An impostor may still pass through onboarding. An attacker may still persuade the help desk to reset someone else’s sign-in method. Organizations need identity verification to help confirm that the person receiving access or requesting a change is the person they intended to authorize.

‍

What Verified Workforce Identity Means in Practice


Verified workforce identity means establishing who a person is when the organization issues access, then re-verifying that identity before high-risk actions. Organizations should choose identity checks based on the action’s risk and retain a record of the verification result.

‍

A practical identity verification flow can include:
‍

  • Government-issued document verification to check authenticity and signs of tampering.
  • A selfie matched to the document portrait to connect the person presenting the document to the claimed identity.
  • Liveness, presentation-attack detection, and injection attack detection to help confirm that a real person is present rather than a photo, replay, mask, or injected image.
  • Source and device signals that add evidence when the workflow requires more than a document and selfie.

‍

These capabilities provide a starting point for comparing employee identity verification solutions for onboarding and account recovery.

‍

Assurance frameworks can help define requirements for these workflows: IAL2 addresses identity proofing, while AAL2 addresses authentication. Organizations still need clear policies for when to verify identity, how to handle data, and how to act on verification results.

‍

Ultimately, no single check establishes identity on its own. A multi-layered approach to identity proofing evaluates the signals together to help confirm that a live person matches the claimed identity and that the supporting information is consistent.

‍

Workforce Identity Verification Across the Employee Lifecycle


Not every action requires identity re-verification. Organizations should apply stronger checks when unauthorized access could expose sensitive data, move money, or change critical systems.

‍

  • Hire: Verify the person before the organization creates a workforce identity, especially for remote, contractor, vendor, and sensitive-role onboarding.
  • First-day provisioning: Use the onboarding verification result to confirm who receives the device, account, or authenticator.
  • Privileged or financial actions: Step up identity assurance before an administrator changes production access, a finance user changes payment details, or an executive account performs a sensitive action.
  • Help desk recovery: Re-verify the caller before resetting a password, replacing an MFA factor, or changing a recovery channel.
  • Contractor and vendor access: Apply a clear, risk-based policy instead of assuming that third-party status justifies weaker proofing.

‍

Organizations can use employee verification to match each stage of the workforce lifecycle with the identity checks it requires. The goal is to verify identity before granting access, restoring access, or approving sensitive changes—not before every action.

‍

Questions to Ask About Your Own Environment

‍

  • What does our help desk verify before the team resets a password or replaces an MFA factor?
  • How did we verify the identities of our last 50 hires, and what evidence do we retain?
  • What happens when an employee loses every authentication factor at once?
  • Which actions trigger re-verification before a privileged account, payment workflow, or recovery channel changes?

‍

How CLEAR1 Verifies Workforce Identity


CLEAR1 strengthens workforce security by verifying the person beyond the device. Its multi-layered approach combines biometric, document, and device signals with verified data sources to help confirm that employees and contractors are who they claim to be—during onboarding, account recovery, and other critical workforce moments.

‍

After a one-time setup, people can re-verify with a selfie when they need help restoring access or completing a sensitive action. Organizations can confirm identity again without requiring people to repeat the full document-verification process.

‍

Through integrations with leading IAM platforms and enterprise systems, CLEAR1 brings these checks into the tools teams already use. This approach extends workforce identity assurance beyond onboarding to help desk support, account recovery, and privileged access—without replacing existing infrastructure.

‍

Request a CLEAR1 demo

Maximize security, minimize friction with CLEAR

Reach out to uncover what problems you can solve when you solve for identity.

By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
blog

How Identity Fraud Enters Through Your Workforce

October 28, 2026

What Identity Fraud Looks Like Inside an Enterprise

‍

Workforce identity fraud occurs when someone uses stolen or fabricated identity information, compromised credentials, or false employment details to gain access to an organization or its systems.

‍

Consumer identity theft often involves opening accounts or obtaining services in another person’s name. In an enterprise, attackers can exploit hiring, support, or recovery workflows to obtain workforce access—even when the account looks normal and the credential is valid.

‍

Identity security protects accounts, credentials, and access through controls such as workforce identity and access management. Identity verification confirms who a person is before organizations grant access or approve a high-risk action. Authentication checks whether someone can present an enrolled credential, but doesn’t establish that the right person enrolled the account or is requesting recovery.

‍

These identity checks matter before suspicious activity appears. By the time detection tools raise an alert, an attacker may already have passed through hiring or persuaded the help desk to restore access.

‍

Why the Workforce is the Entry Point

‍

Attackers don’t always need to steal a password or bypass MFA. Weak identity checks during hiring or account recovery can lead an organization to issue valid credentials to an impostor.

‍

Protecting accounts and devices doesn’t replace verifying the employees, contractors, and vendors requesting access. Even with phishing-resistant authentication, organizations still need to answer three critical identity questions:
‍

  • Is the person applying for a role the person they claim to be?
  • Is the person requesting an MFA factor replacement authorized to make that request?
  • Is the person requesting account recovery the person who should receive a new credential?

‍

Three Common Moments Where Fraud Enters the Workplace


Three workflows deserve particular attention: onboarding, when organizations grant access; help desk recovery, when agents decide whether to restore access; and self-service recovery, when systems restore access without an agent. Each workflow starts with a claim about who the person is. Identity verification helps confirm that the person requesting access is who they say they are.

‍

1. Onboarding


Document reviews, video interviews, and work eligibility checks don’t necessarily establish that the person interviewed is the person who ultimately receives access. This leaves organizations vulnerable to fraudulent applicants, interview substitution, synthetic or deepfaked candidates, and impersonated contractors.

‍

Remote hiring fraud is a documented risk, not a hypothetical one. In a July 31, 2026 joint alert, the U.S. State Department, FBI, and international partners warned that North Korean IT workers use forged identity documents and third-party proxies to obtain remote work. Proxies may even participate in interviews while someone else performs the job. The alert urges online employment and contracting platforms to strengthen identity verification procedures. 

‍

A verified onboarding flow, as part of a broader Know Your Employee approach, connects the person to the identity document, confirms that a live person is present, and checks supporting signals before provisioning access. This matters in cases of synthetic identity fraud, where attackers combine real and fabricated information to create an identity that appears legitimate.

‍

2. Help Desk Recovery


Help desks may ask for an employee ID, manager’s name, start date, or the last four digits of a government identifier. Those answers can show familiarity with an employee’s information without establishing the caller’s identity.

‍

Social engineering exploits the pressure to restore access quickly. The workflow asks help desk agents to make an identity decision with weak evidence.

‍

Rather than rely on those answers alone, the help desk agent can initiate document and selfie verification before restoring access. The caller presents a government-issued document and takes a selfie. The system checks document authenticity, liveness, and whether the selfie matches the document photo. The agent can then apply the organization’s recovery policy using verified identity information rather than answers to personal questions.

‍

3. Self-Service Account Recovery


Self-service recovery exists because users forget passwords or lose access to phones, security keys, or authenticator apps. But if the process relies on a compromised mailbox, an attacker-controlled phone number, a stolen backup code, or a security question the attacker can answer, the attacker can reset credentials and take over the account.

‍

When normal authentication fails, organizations should verify the person requesting account recovery before restoring access. Depending on the risk, verification can include document checks, biometric matching, liveness detection, source validation, and device security signals. Stronger identity checks are particularly important before replacing an MFA factor or changing a recovery channel, especially for privileged accounts.

‍

Why MFA Can’t Verify the Person Behind the Credential


MFA, passwordless sign-in, and phishing-resistant methods strengthen account security, but stronger authentication won’t fix access granted to the wrong person. An impostor may still pass through onboarding. An attacker may still persuade the help desk to reset someone else’s sign-in method. Organizations need identity verification to help confirm that the person receiving access or requesting a change is the person they intended to authorize.

‍

What Verified Workforce Identity Means in Practice


Verified workforce identity means establishing who a person is when the organization issues access, then re-verifying that identity before high-risk actions. Organizations should choose identity checks based on the action’s risk and retain a record of the verification result.

‍

A practical identity verification flow can include:
‍

  • Government-issued document verification to check authenticity and signs of tampering.
  • A selfie matched to the document portrait to connect the person presenting the document to the claimed identity.
  • Liveness, presentation-attack detection, and injection attack detection to help confirm that a real person is present rather than a photo, replay, mask, or injected image.
  • Source and device signals that add evidence when the workflow requires more than a document and selfie.

‍

These capabilities provide a starting point for comparing employee identity verification solutions for onboarding and account recovery.

‍

Assurance frameworks can help define requirements for these workflows: IAL2 addresses identity proofing, while AAL2 addresses authentication. Organizations still need clear policies for when to verify identity, how to handle data, and how to act on verification results.

‍

Ultimately, no single check establishes identity on its own. A multi-layered approach to identity proofing evaluates the signals together to help confirm that a live person matches the claimed identity and that the supporting information is consistent.

‍

Workforce Identity Verification Across the Employee Lifecycle


Not every action requires identity re-verification. Organizations should apply stronger checks when unauthorized access could expose sensitive data, move money, or change critical systems.

‍

  • Hire: Verify the person before the organization creates a workforce identity, especially for remote, contractor, vendor, and sensitive-role onboarding.
  • First-day provisioning: Use the onboarding verification result to confirm who receives the device, account, or authenticator.
  • Privileged or financial actions: Step up identity assurance before an administrator changes production access, a finance user changes payment details, or an executive account performs a sensitive action.
  • Help desk recovery: Re-verify the caller before resetting a password, replacing an MFA factor, or changing a recovery channel.
  • Contractor and vendor access: Apply a clear, risk-based policy instead of assuming that third-party status justifies weaker proofing.

‍

Organizations can use employee verification to match each stage of the workforce lifecycle with the identity checks it requires. The goal is to verify identity before granting access, restoring access, or approving sensitive changes—not before every action.

‍

Questions to Ask About Your Own Environment

‍

  • What does our help desk verify before the team resets a password or replaces an MFA factor?
  • How did we verify the identities of our last 50 hires, and what evidence do we retain?
  • What happens when an employee loses every authentication factor at once?
  • Which actions trigger re-verification before a privileged account, payment workflow, or recovery channel changes?

‍

How CLEAR1 Verifies Workforce Identity


CLEAR1 strengthens workforce security by verifying the person beyond the device. Its multi-layered approach combines biometric, document, and device signals with verified data sources to help confirm that employees and contractors are who they claim to be—during onboarding, account recovery, and other critical workforce moments.

‍

After a one-time setup, people can re-verify with a selfie when they need help restoring access or completing a sensitive action. Organizations can confirm identity again without requiring people to repeat the full document-verification process.

‍

Through integrations with leading IAM platforms and enterprise systems, CLEAR1 brings these checks into the tools teams already use. This approach extends workforce identity assurance beyond onboarding to help desk support, account recovery, and privileged access—without replacing existing infrastructure.

‍

Request a CLEAR1 demo

More product updates

VIEW ALL RELEASE NOTES
No items found.
blog

How Identity Fraud Enters Through Your Workforce

October 28, 2026

What Identity Fraud Looks Like Inside an Enterprise

‍

Workforce identity fraud occurs when someone uses stolen or fabricated identity information, compromised credentials, or false employment details to gain access to an organization or its systems.

‍

Consumer identity theft often involves opening accounts or obtaining services in another person’s name. In an enterprise, attackers can exploit hiring, support, or recovery workflows to obtain workforce access—even when the account looks normal and the credential is valid.

‍

Identity security protects accounts, credentials, and access through controls such as workforce identity and access management. Identity verification confirms who a person is before organizations grant access or approve a high-risk action. Authentication checks whether someone can present an enrolled credential, but doesn’t establish that the right person enrolled the account or is requesting recovery.

‍

These identity checks matter before suspicious activity appears. By the time detection tools raise an alert, an attacker may already have passed through hiring or persuaded the help desk to restore access.

‍

Why the Workforce is the Entry Point

‍

Attackers don’t always need to steal a password or bypass MFA. Weak identity checks during hiring or account recovery can lead an organization to issue valid credentials to an impostor.

‍

Protecting accounts and devices doesn’t replace verifying the employees, contractors, and vendors requesting access. Even with phishing-resistant authentication, organizations still need to answer three critical identity questions:
‍

  • Is the person applying for a role the person they claim to be?
  • Is the person requesting an MFA factor replacement authorized to make that request?
  • Is the person requesting account recovery the person who should receive a new credential?

‍

Three Common Moments Where Fraud Enters the Workplace


Three workflows deserve particular attention: onboarding, when organizations grant access; help desk recovery, when agents decide whether to restore access; and self-service recovery, when systems restore access without an agent. Each workflow starts with a claim about who the person is. Identity verification helps confirm that the person requesting access is who they say they are.

‍

1. Onboarding


Document reviews, video interviews, and work eligibility checks don’t necessarily establish that the person interviewed is the person who ultimately receives access. This leaves organizations vulnerable to fraudulent applicants, interview substitution, synthetic or deepfaked candidates, and impersonated contractors.

‍

Remote hiring fraud is a documented risk, not a hypothetical one. In a July 31, 2026 joint alert, the U.S. State Department, FBI, and international partners warned that North Korean IT workers use forged identity documents and third-party proxies to obtain remote work. Proxies may even participate in interviews while someone else performs the job. The alert urges online employment and contracting platforms to strengthen identity verification procedures. 

‍

A verified onboarding flow, as part of a broader Know Your Employee approach, connects the person to the identity document, confirms that a live person is present, and checks supporting signals before provisioning access. This matters in cases of synthetic identity fraud, where attackers combine real and fabricated information to create an identity that appears legitimate.

‍

2. Help Desk Recovery


Help desks may ask for an employee ID, manager’s name, start date, or the last four digits of a government identifier. Those answers can show familiarity with an employee’s information without establishing the caller’s identity.

‍

Social engineering exploits the pressure to restore access quickly. The workflow asks help desk agents to make an identity decision with weak evidence.

‍

Rather than rely on those answers alone, the help desk agent can initiate document and selfie verification before restoring access. The caller presents a government-issued document and takes a selfie. The system checks document authenticity, liveness, and whether the selfie matches the document photo. The agent can then apply the organization’s recovery policy using verified identity information rather than answers to personal questions.

‍

3. Self-Service Account Recovery


Self-service recovery exists because users forget passwords or lose access to phones, security keys, or authenticator apps. But if the process relies on a compromised mailbox, an attacker-controlled phone number, a stolen backup code, or a security question the attacker can answer, the attacker can reset credentials and take over the account.

‍

When normal authentication fails, organizations should verify the person requesting account recovery before restoring access. Depending on the risk, verification can include document checks, biometric matching, liveness detection, source validation, and device security signals. Stronger identity checks are particularly important before replacing an MFA factor or changing a recovery channel, especially for privileged accounts.

‍

Why MFA Can’t Verify the Person Behind the Credential


MFA, passwordless sign-in, and phishing-resistant methods strengthen account security, but stronger authentication won’t fix access granted to the wrong person. An impostor may still pass through onboarding. An attacker may still persuade the help desk to reset someone else’s sign-in method. Organizations need identity verification to help confirm that the person receiving access or requesting a change is the person they intended to authorize.

‍

What Verified Workforce Identity Means in Practice


Verified workforce identity means establishing who a person is when the organization issues access, then re-verifying that identity before high-risk actions. Organizations should choose identity checks based on the action’s risk and retain a record of the verification result.

‍

A practical identity verification flow can include:
‍

  • Government-issued document verification to check authenticity and signs of tampering.
  • A selfie matched to the document portrait to connect the person presenting the document to the claimed identity.
  • Liveness, presentation-attack detection, and injection attack detection to help confirm that a real person is present rather than a photo, replay, mask, or injected image.
  • Source and device signals that add evidence when the workflow requires more than a document and selfie.

‍

These capabilities provide a starting point for comparing employee identity verification solutions for onboarding and account recovery.

‍

Assurance frameworks can help define requirements for these workflows: IAL2 addresses identity proofing, while AAL2 addresses authentication. Organizations still need clear policies for when to verify identity, how to handle data, and how to act on verification results.

‍

Ultimately, no single check establishes identity on its own. A multi-layered approach to identity proofing evaluates the signals together to help confirm that a live person matches the claimed identity and that the supporting information is consistent.

‍

Workforce Identity Verification Across the Employee Lifecycle


Not every action requires identity re-verification. Organizations should apply stronger checks when unauthorized access could expose sensitive data, move money, or change critical systems.

‍

  • Hire: Verify the person before the organization creates a workforce identity, especially for remote, contractor, vendor, and sensitive-role onboarding.
  • First-day provisioning: Use the onboarding verification result to confirm who receives the device, account, or authenticator.
  • Privileged or financial actions: Step up identity assurance before an administrator changes production access, a finance user changes payment details, or an executive account performs a sensitive action.
  • Help desk recovery: Re-verify the caller before resetting a password, replacing an MFA factor, or changing a recovery channel.
  • Contractor and vendor access: Apply a clear, risk-based policy instead of assuming that third-party status justifies weaker proofing.

‍

Organizations can use employee verification to match each stage of the workforce lifecycle with the identity checks it requires. The goal is to verify identity before granting access, restoring access, or approving sensitive changes—not before every action.

‍

Questions to Ask About Your Own Environment

‍

  • What does our help desk verify before the team resets a password or replaces an MFA factor?
  • How did we verify the identities of our last 50 hires, and what evidence do we retain?
  • What happens when an employee loses every authentication factor at once?
  • Which actions trigger re-verification before a privileged account, payment workflow, or recovery channel changes?

‍

How CLEAR1 Verifies Workforce Identity


CLEAR1 strengthens workforce security by verifying the person beyond the device. Its multi-layered approach combines biometric, document, and device signals with verified data sources to help confirm that employees and contractors are who they claim to be—during onboarding, account recovery, and other critical workforce moments.

‍

After a one-time setup, people can re-verify with a selfie when they need help restoring access or completing a sensitive action. Organizations can confirm identity again without requiring people to repeat the full document-verification process.

‍

Through integrations with leading IAM platforms and enterprise systems, CLEAR1 brings these checks into the tools teams already use. This approach extends workforce identity assurance beyond onboarding to help desk support, account recovery, and privileged access—without replacing existing infrastructure.

‍

Request a CLEAR1 demo

What Identity Fraud Looks Like Inside an Enterprise

‍

Workforce identity fraud occurs when someone uses stolen or fabricated identity information, compromised credentials, or false employment details to gain access to an organization or its systems.

‍

Consumer identity theft often involves opening accounts or obtaining services in another person’s name. In an enterprise, attackers can exploit hiring, support, or recovery workflows to obtain workforce access—even when the account looks normal and the credential is valid.

‍

Identity security protects accounts, credentials, and access through controls such as workforce identity and access management. Identity verification confirms who a person is before organizations grant access or approve a high-risk action. Authentication checks whether someone can present an enrolled credential, but doesn’t establish that the right person enrolled the account or is requesting recovery.

‍

These identity checks matter before suspicious activity appears. By the time detection tools raise an alert, an attacker may already have passed through hiring or persuaded the help desk to restore access.

‍

Why the Workforce is the Entry Point

‍

Attackers don’t always need to steal a password or bypass MFA. Weak identity checks during hiring or account recovery can lead an organization to issue valid credentials to an impostor.

‍

Protecting accounts and devices doesn’t replace verifying the employees, contractors, and vendors requesting access. Even with phishing-resistant authentication, organizations still need to answer three critical identity questions:
‍

  • Is the person applying for a role the person they claim to be?
  • Is the person requesting an MFA factor replacement authorized to make that request?
  • Is the person requesting account recovery the person who should receive a new credential?

‍

Three Common Moments Where Fraud Enters the Workplace


Three workflows deserve particular attention: onboarding, when organizations grant access; help desk recovery, when agents decide whether to restore access; and self-service recovery, when systems restore access without an agent. Each workflow starts with a claim about who the person is. Identity verification helps confirm that the person requesting access is who they say they are.

‍

1. Onboarding


Document reviews, video interviews, and work eligibility checks don’t necessarily establish that the person interviewed is the person who ultimately receives access. This leaves organizations vulnerable to fraudulent applicants, interview substitution, synthetic or deepfaked candidates, and impersonated contractors.

‍

Remote hiring fraud is a documented risk, not a hypothetical one. In a July 31, 2026 joint alert, the U.S. State Department, FBI, and international partners warned that North Korean IT workers use forged identity documents and third-party proxies to obtain remote work. Proxies may even participate in interviews while someone else performs the job. The alert urges online employment and contracting platforms to strengthen identity verification procedures. 

‍

A verified onboarding flow, as part of a broader Know Your Employee approach, connects the person to the identity document, confirms that a live person is present, and checks supporting signals before provisioning access. This matters in cases of synthetic identity fraud, where attackers combine real and fabricated information to create an identity that appears legitimate.

‍

2. Help Desk Recovery


Help desks may ask for an employee ID, manager’s name, start date, or the last four digits of a government identifier. Those answers can show familiarity with an employee’s information without establishing the caller’s identity.

‍

Social engineering exploits the pressure to restore access quickly. The workflow asks help desk agents to make an identity decision with weak evidence.

‍

Rather than rely on those answers alone, the help desk agent can initiate document and selfie verification before restoring access. The caller presents a government-issued document and takes a selfie. The system checks document authenticity, liveness, and whether the selfie matches the document photo. The agent can then apply the organization’s recovery policy using verified identity information rather than answers to personal questions.

‍

3. Self-Service Account Recovery


Self-service recovery exists because users forget passwords or lose access to phones, security keys, or authenticator apps. But if the process relies on a compromised mailbox, an attacker-controlled phone number, a stolen backup code, or a security question the attacker can answer, the attacker can reset credentials and take over the account.

‍

When normal authentication fails, organizations should verify the person requesting account recovery before restoring access. Depending on the risk, verification can include document checks, biometric matching, liveness detection, source validation, and device security signals. Stronger identity checks are particularly important before replacing an MFA factor or changing a recovery channel, especially for privileged accounts.

‍

Why MFA Can’t Verify the Person Behind the Credential


MFA, passwordless sign-in, and phishing-resistant methods strengthen account security, but stronger authentication won’t fix access granted to the wrong person. An impostor may still pass through onboarding. An attacker may still persuade the help desk to reset someone else’s sign-in method. Organizations need identity verification to help confirm that the person receiving access or requesting a change is the person they intended to authorize.

‍

What Verified Workforce Identity Means in Practice


Verified workforce identity means establishing who a person is when the organization issues access, then re-verifying that identity before high-risk actions. Organizations should choose identity checks based on the action’s risk and retain a record of the verification result.

‍

A practical identity verification flow can include:
‍

  • Government-issued document verification to check authenticity and signs of tampering.
  • A selfie matched to the document portrait to connect the person presenting the document to the claimed identity.
  • Liveness, presentation-attack detection, and injection attack detection to help confirm that a real person is present rather than a photo, replay, mask, or injected image.
  • Source and device signals that add evidence when the workflow requires more than a document and selfie.

‍

These capabilities provide a starting point for comparing employee identity verification solutions for onboarding and account recovery.

‍

Assurance frameworks can help define requirements for these workflows: IAL2 addresses identity proofing, while AAL2 addresses authentication. Organizations still need clear policies for when to verify identity, how to handle data, and how to act on verification results.

‍

Ultimately, no single check establishes identity on its own. A multi-layered approach to identity proofing evaluates the signals together to help confirm that a live person matches the claimed identity and that the supporting information is consistent.

‍

Workforce Identity Verification Across the Employee Lifecycle


Not every action requires identity re-verification. Organizations should apply stronger checks when unauthorized access could expose sensitive data, move money, or change critical systems.

‍

  • Hire: Verify the person before the organization creates a workforce identity, especially for remote, contractor, vendor, and sensitive-role onboarding.
  • First-day provisioning: Use the onboarding verification result to confirm who receives the device, account, or authenticator.
  • Privileged or financial actions: Step up identity assurance before an administrator changes production access, a finance user changes payment details, or an executive account performs a sensitive action.
  • Help desk recovery: Re-verify the caller before resetting a password, replacing an MFA factor, or changing a recovery channel.
  • Contractor and vendor access: Apply a clear, risk-based policy instead of assuming that third-party status justifies weaker proofing.

‍

Organizations can use employee verification to match each stage of the workforce lifecycle with the identity checks it requires. The goal is to verify identity before granting access, restoring access, or approving sensitive changes—not before every action.

‍

Questions to Ask About Your Own Environment

‍

  • What does our help desk verify before the team resets a password or replaces an MFA factor?
  • How did we verify the identities of our last 50 hires, and what evidence do we retain?
  • What happens when an employee loses every authentication factor at once?
  • Which actions trigger re-verification before a privileged account, payment workflow, or recovery channel changes?

‍

How CLEAR1 Verifies Workforce Identity


CLEAR1 strengthens workforce security by verifying the person beyond the device. Its multi-layered approach combines biometric, document, and device signals with verified data sources to help confirm that employees and contractors are who they claim to be—during onboarding, account recovery, and other critical workforce moments.

‍

After a one-time setup, people can re-verify with a selfie when they need help restoring access or completing a sensitive action. Organizations can confirm identity again without requiring people to repeat the full document-verification process.

‍

Through integrations with leading IAM platforms and enterprise systems, CLEAR1 brings these checks into the tools teams already use. This approach extends workforce identity assurance beyond onboarding to help desk support, account recovery, and privileged access—without replacing existing infrastructure.

‍

Request a CLEAR1 demo

PARTNER SPOTLIGHT
INDUSTRY
Workforce
COMPANY SIZE
INDUSTRY
Workforce
COMPANY SIZE

Maximize security, minimize friction with CLEAR

Reach out to uncover what problems you can solve when you solve for identity.

By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
blog
Person looking at CLEAR Multi-Layered Identity Screen
By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
Gartner®, Deepfake Identity Threats: Mitigate Risk in Identity Verification and Face Biometrics, Akif Khan, Nayara Sangiorgio, James Hoover, 11 May 2026

‍Gartner® is a trademark of Gartner, Inc. and/or its affiliates.
blog
By submitting my personal data, I consent to CLEAR collecting, processing, and storing my information in accordance with the CLEAR Privacy Notice.
Thank you! You are being redirected

Thank you! View the webinar below.

Oops! Something went wrong while submitting the form.
blog

How Identity Fraud Enters Through Your Workforce

October 28, 2026

More webinars

VIEW ALL WEBINARS
No items found.